
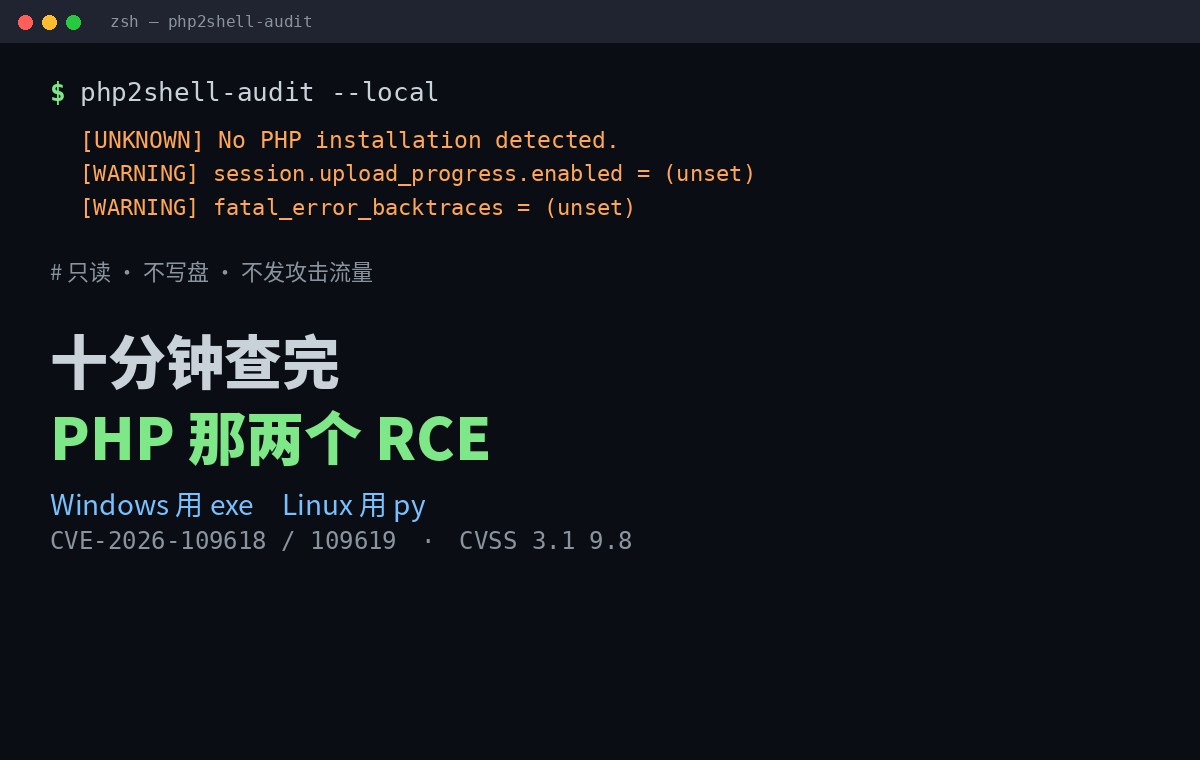
php2shell-audit field: Windows uses exe, Linux, py, 10 minutes to figure out PHP.
It's not about bends. It's all about knocks:Loading tools, running machines, cleaning targets, reading conclusions, deciding whether or not to patchA dragon. Ten minutes to finish.
First, CVE-2026-109618 and CVE-2026-109619 are unauthorized RCE for the PHP engine itself, the official restored version is 8.2.35 / 8.3.36 / 8.4.27 / 8.5.12. Two sets of caliber...PHP official CVSS 4.0 beat 9.2, NVD CVSS 3.1 beat 9.89.8 in the title is the latter, and both refer to the same two-to-one loophole, not to think it's different.
Here are the tools:Vivipenclaw-code/php2shell-uditApache-2.0, just today. It does two things: check what PHPs are installed on this machine, sweep the undiscovered version of the far-off storm.It does not attack traffic, does not write discs, does not change any configuration.And that's what I've checked in the source code, and the remote mode is really only sending one HEAD request for a response head.
I. DIFTING: Two ways to see which system you're in.
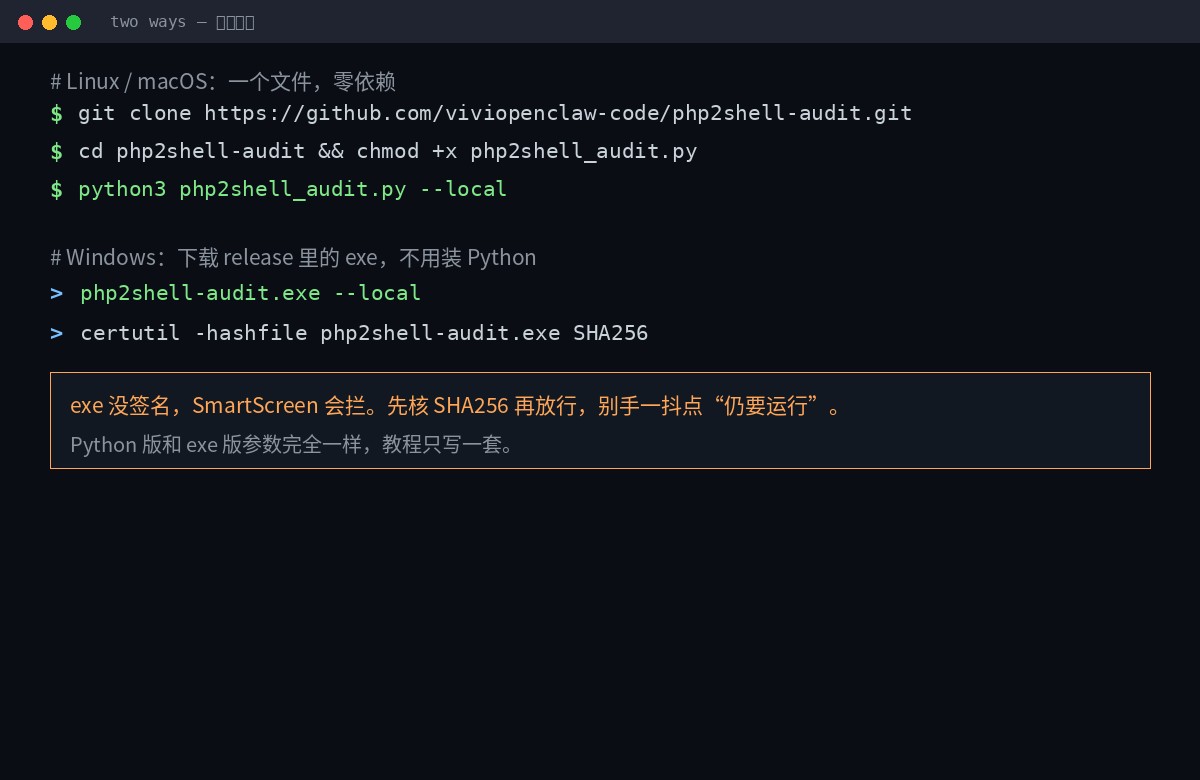
Linux / MacOS go Python, zero dependency, standard library is enough, no pip to load anything:
git clone https://github.com/viviopenclaw-code/php2shell-audit.git
cd php2shell-audit
chmod +x php2shell_audit.py
python3 php2shell_audit.py --local
Windows goes straight to the exe, without Python. Grab on release page php2shell-audit.exe:
certutil -hashfile php2shell-audit.exe SHA256
php2shell-audit.exe --local
Exe is a single file console program that Win10/11 x64 is available,No code signature.So the first run for SmartScreen would stop. Let's run first. SHA256SUMS.txt Once again — this step is one in which no one touches the “green” version that is being circulated online.
Two versions of the same parameters. Only one set at the back of the tutorial, Windows. python3 php2shell_audit.py Replace php2shell-audit.exe Just do it.
What's going on?
python3 php2shell_audit.py --localIt'll do four things, one thing:
- Find PHP.:
/usr/bin/php*I don't know./usr/sbin/php-fpm*I don't know./opt/*I don't know./usr/lib/php/*/sapi/*Homebrew also counts. Windows, check it out.C:\phpPHP under XAMPP, WAMP, Laragon, Chocolatey, Scoop, Program Files. - Read Version: Run
php -vTake Banner, with 8.2.35 / 8.3.36 / 8.4.27 / 8.5.12. - Check Configuration: parsing the interim mitigation instructions in php.ini.
- Column Process: list all the works that must be restarted after the patch.
I ran over a machine without a PHP. Here's the output:
php2shell-audit 1.1.0 - local audit
Host    : admin
System  : Linux 7.0.0-30-generic (x86_64)
------------------------------------------------------------------------
[UNKNOWN] No PHP installation detected.
------------------------------------------------------------------------
php.ini mitigation directives
[WARNING] session.upload_progress.enabled = (unset)  (recommended 0)
[WARNING] fatal_error_backtraces = (unset)  (recommended 0)
[WARNING] expose_php = (unset)  (recommended 0)
------------------------------------------------------------------------
Running services that must be restarted after patching
[INFO] apache2 - 3 process(es)
------------------------------------------------------------------------
[INFO] No PHP binary, FPM daemon or Apache PHP module was found on this host.
------------------------------------------------------------------------
Remediation
[UNKNOWN] No PHP install was audited, so nothing can be confirmed safe.
Watch the last line:No PHP it's UNKNOWN, no PASS.This design is very well-recognised -- there's no problem with finding anything. It's two different things.
By the way, it's connected. expose_php All of them. This one has nothing to do with the loophole itself, but it's a direct decision as to whether a remote scan can read your version number.Turn it off. The assailant's fingerprints are half blind.I don't know. Of course, it's not called repair, it's called reducing information exposure.
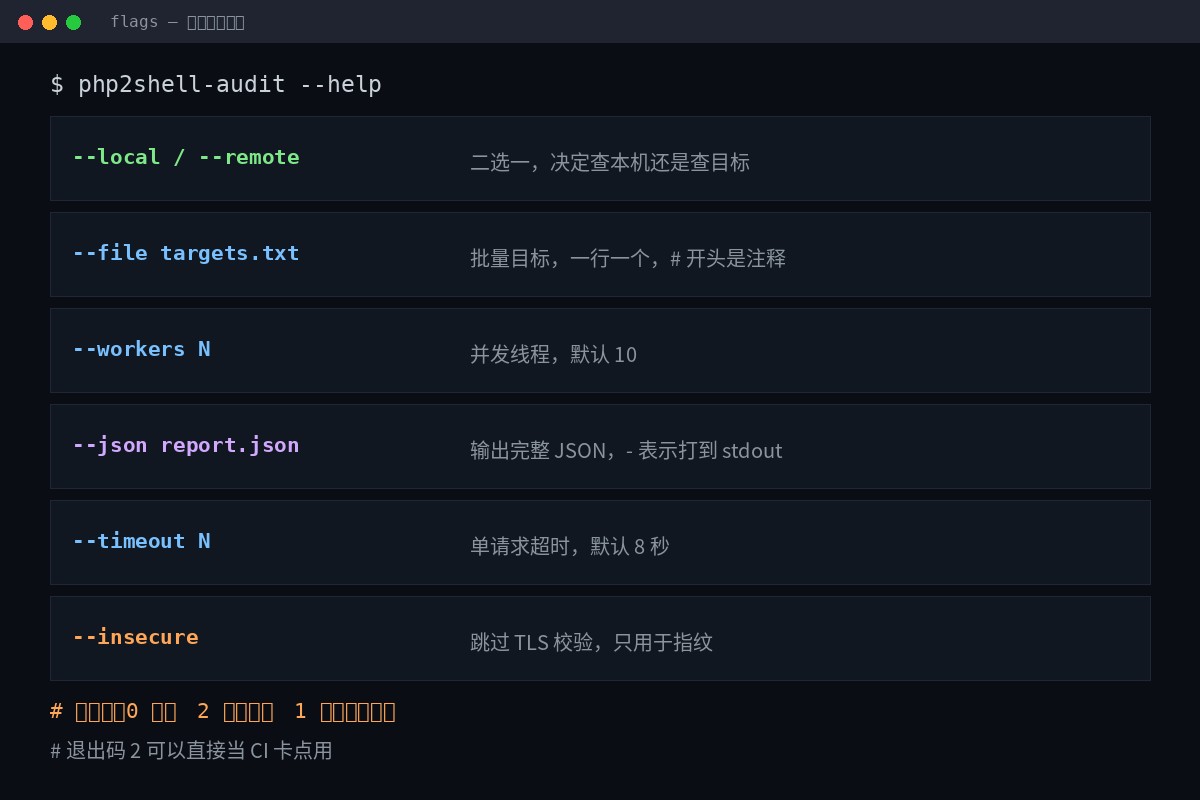
III. Parameters
| Parameters | Role | Default |
|---|---|---|
--local / --remote | Two or one, we decide to check the machine or target. | Required |
--file targets.txt | Batch target, one in one row, # start with comment | None |
--workers N | Number of long-term concurrent courses | 10 |
--json report.json | Output complete JSON,- Hit to stdout | None |
--timeout N | Single request timeout (sec) | 8 |
--insecure | Skip TLS verification, only for fingerprints | Close |
Exit code: direct to the CI card point
| Exit Code | Meaning |
|---|---|
0 | No affected version found |
2 | At least one affected version was found. |
1 | Error on the tool itself (e. g. JSON cannot write) |
Quit number two, this is the point.It means you can put it in the flow line, sweep it through the construction phase, hit it, and don't wait for humans to find it.
iv. Sweeping remote: –remote how
# 单个目标
python3 php2shell_audit.py --remote example.com

# 批量,20 个并发,出 JSON
python3 php2shell_audit.py --remote --file targets.txt --workers 20 --json out.json

# 也可以直接写在命令行里
python3 php2shell_audit.py --remote https://a.example 10.0.0.5
What? Write
# production fleet
example.com
https://shop.example.net
10.0.0.5:8080
# Start with a note, one line, one in the warehouse targets.example.txt It can be copied directly.
What did it send?
Every goal.Send only one HEAD request, only once will the server reject HeAD. And read it. Server:I don't know.X-Powered-By: and Set-CookieGet out of there. PHP/x.y.zI don't know.
No multipart, no big body, no OOM, no use-after-free.It died in the source note as a design constraint.It's not random.
The price must be clear:Remote mode does not prove usabilityIt can only report information that the server voluntarily spits out. Hide the version number's target, and the result will always be UNKNOWN.
V. How to read the conclusions
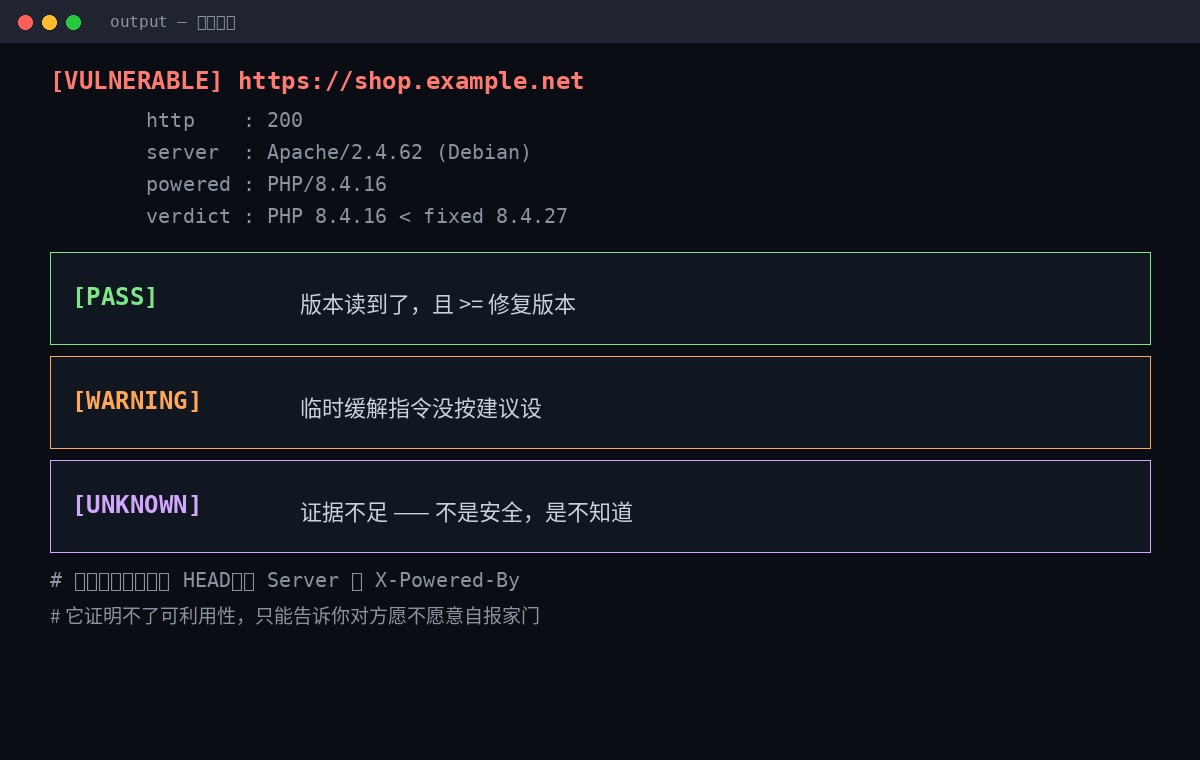
[VULNERABLE] https://shop.example.net
         http    : 200
         server  : Apache/2.4.62 (Debian)
         powered : PHP/8.4.16
         php     : 8.4.16
verdict : PHP 8.4.16 < fixed 8.4.27- [VULNERABLE] The version was read and lower than the restored version.
- [PASS] The version was read and is greater than or equal to the restored version.
- [WARNING] The interim mitigation instructions were not set as suggested.
- [UNKNOWN] Insufficient evidence.Not safe, not known.
This distinction is where the whole tool is most valuable. Most scanners only give you red, yellow and green, and then you think it's all over the screen.UNKNOWN must be considered to-doEither turn off the hidden version, run in the container -- local, or log on to the machine.
Six, four pits, one more than the other.
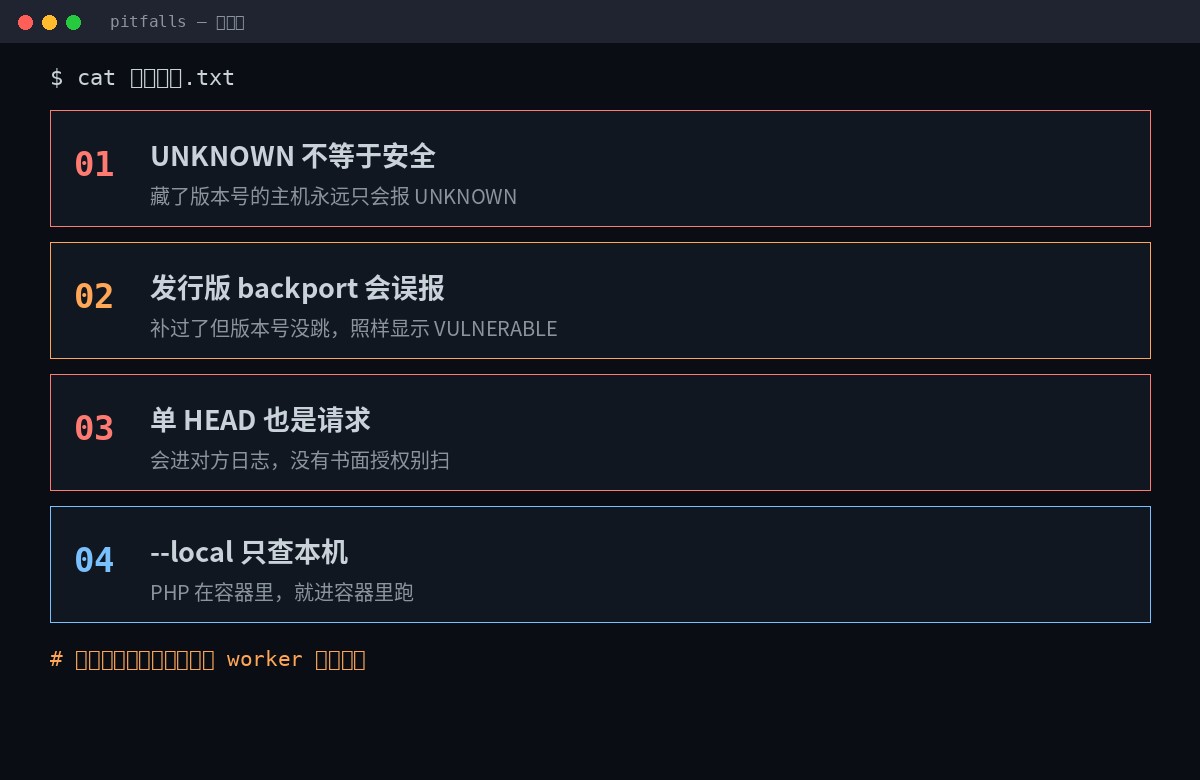
Pipe 1: UNKNOWN ≠ Clear
The host that hid the version number will always report UNKNOWN. Just make sure it's only on the mainframe. --localI don't know.
Pocket 2: Release is misreported.
Debian / Ubuntu / RHEL / Alpine regularly calls in safety patches butDo Not Jump Version NumberI don't know. The result is the completed machine, as it appears.
So don't panic until you see the red.
apt changelog php8.4
rpm -q --changelog php-8.4 | head -50
This step, or failure to do so, would be nothing but an escalation; it would also be a miscalculation, which is the real need for an upgrade.
Pit 3: A HEAD is also requested
It'll be in each other's log, and it'll be written down by WAF. Sweeping without a written authorization is by nature an unauthorized detection - a law such as the CFAA, the UK CMA 1990.
I'll need authorization to clean up my company's assets.In particular, cross-sectoral, cross-sub-company, cloud-based accounts. Don't think, "I'm just looking at a response head" doesn't count.
Pocket 4:-local only check the machine.
PHP runs in the container, runs in the container, or uses it on the host. --remote The port that was mapped out. The host runs. --local If you can't find the PHP in the container, you'll get a UNKNOWN -- the UNKNOWN really doesn't know, not the container is safe.
Seven, find out there's a problem, then what?
Patching is the only complete repair.All the rest is bleeding.
# Debian / Ubuntu
sudo apt update && sudo apt install --only-upgrade php

# RHEL / Fedora
sudo dnf upgrade 'php*'

# Alpine
sudo apk upgrade php83 php84
Upgrade: 8.2 branch to 8.2.358.3 to 8.3.36It's 8.4. 8.4.27It's 8.5. 8.5.12I don't know. 8.1 and beyond, only source level report.
If you can't get a patch, do these first, then start all over again.
; CVE-2026-109619
session.upload_progress.enabled = 0

; CVE-2026-109618
memory_limit = -1

; 仅 PHP 8.5
fatal_error_backtraces = 0session.upload_progress.enabled=0To be written in php.ini, FPM tool or server configuration,It has to be effective before the request.I don't know. It's too late.memory_limit=-1I need it.php_admin_valueThe level setting of such applications is unchanged, while ensuring that there is no pool/ directory/ application to restore the limited value.- Never use RLIMIT AS or RLIMIT DATA- Those two will make Map fail and just re-enter that dangerous longjmp path.
- Change must restart every worker:
systemctl restart php*-fpm apache2 nginxI don't know.No restart is no change.
None of these four can make you safe, and the authorities themselves are quite clear. They have only one value:Before you patch it, cover the door.
VIII. A complete sequence
- Check yourself first.:
--localThree or five seconds, see the version and configuration. - Remote batch sweepIt's a big deal.
--remote --fileAnd run, out of JSON. - Classification processing:VULNERABLE upgrade, WARNING replenishment, UNKNOWN identification --It's not closed, it's to be done.
- Upgrade + Restart Worker: Patches, and then restart all FPM/ Apache/ nginx.
- Resweep Authentication: Run again, confirm green. Watch the backport error and watch changelog if necessary.
- Get in the water line.: Quit Code 2 Direct fail construction, and next time no one will remember.
The whole process is ten minutes, and the real time is the third step.Check the UNKNOWN lines.I don't know. But that's not gonna save it, because skipping it, you get a pretty, fake, green report.
The value of the scanner isn't giving you green lights, it's forcing you to admit where you don't really know.
Replay the project address:Gythub.com/viviopenclaw-code/php2shell-uditI don't know. Read DISSLAIMER.md before it's written in Chinese.
Last sentence reminds me that this tool is 1.1.0 today, the first public version, a single zero fork, a small number of codes, you can read them all. php2shell_audit.pyI don't know.Look at the source code., especially if you want to read the php.ini and the process list with administrator permission.