
AI, breaching Anthropic took only 12 hours: not the model, but the office software it bought.
Let's get this straight:It's not an invasion. It's an authorized test.Cathedral did this in the leak reporting project that Anthropic set up himself (the authorized channel for external researchers), and it was reported to each other in a process. The word "break-through" is a powerful word, but it can lead to misjudgement of the nature of the risk.
The number of "12 hours" is not really worth looking at. Another more simple question:Where was a company that made the model safe for the industry?The answer is -- from the office software it bought.
The value of this is here: it turns "supply chain security" from the right word to a specific path that can be drawn.
I. Factual level: who, what, what to get
Cathedral is a security company that has been in existence for several months, and four co-founders, Gavin Kliger, Luke Farritor, Marko Elez and Jack Stein, were former DoGE staffer, and Kliger was the chief data officer of the Pentagon. Reuters reported in July that it had melted $160 million, valued at $1.4 billion, and received a16z and Sequoia.
It submitted a copy to Anthropic.Draft report(draft report), read in the Washington Post. So all the details below are premised on:It is a document that may be modified and is not independently verified by third parties.
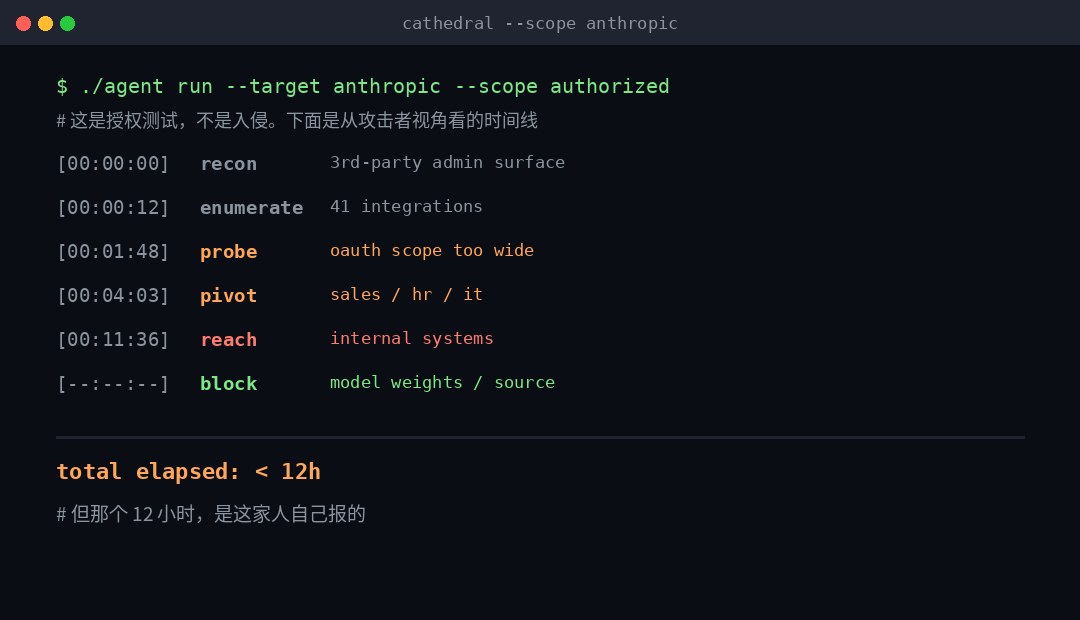
Route: Go around the model, go through office software
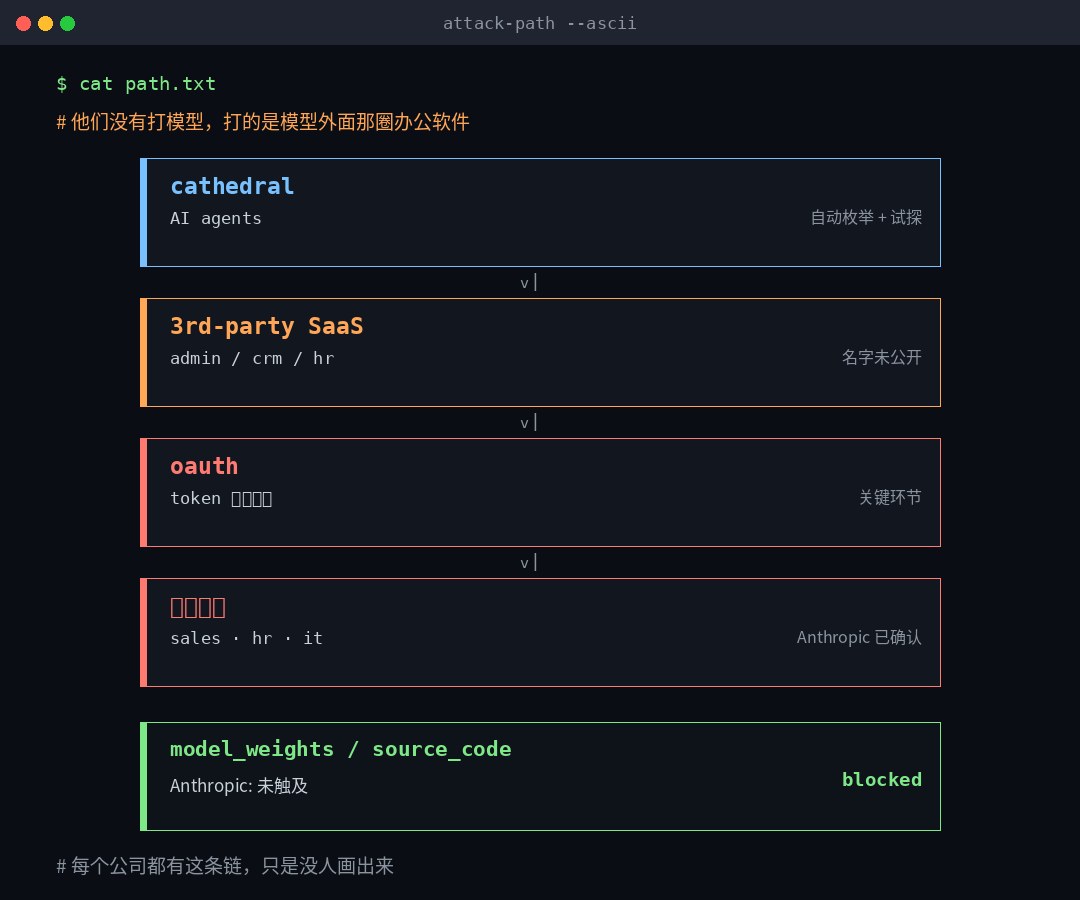
According to the report: AI smart body is passed in less than 12 hoursThird-party management softwareWeaknesses have found a way into the internal system. Sales, people, IT, these types of backstage tools, they're not model infrastructure, they're not the code that Anthony wrote himself.
The name of the software manufacturer involved and the specific loopholes, both parties chose not to disclose, citing fear of abuse. This has prevented external review, but it is also consistent with the usual practice of disclosing loopholes.
Two: the things you get, the things you don't get.
This recommendation is complete, because the most widely disseminated sentence on social media, "Slack with an internal discussion of advanced models", was actually intercepted.
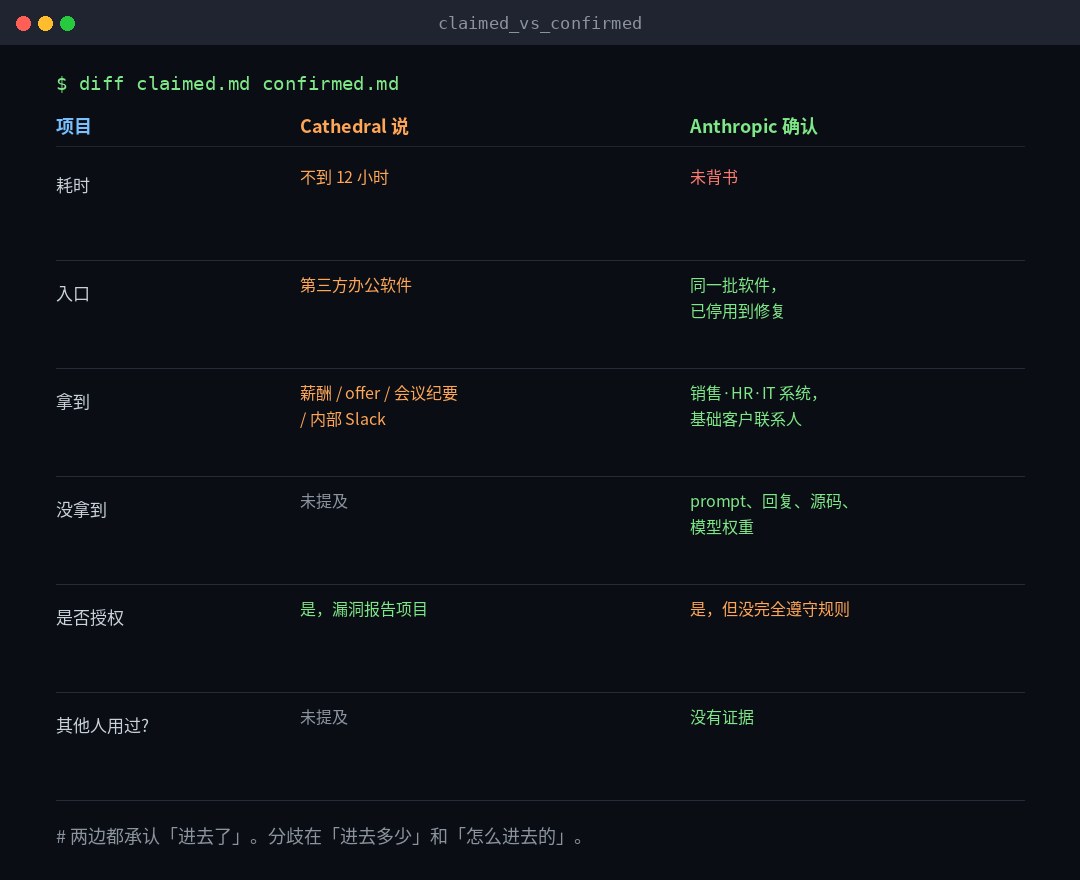
| Catedral, report. | Anthropic confirmed range | |
|---|---|---|
| Operational data | Staff remuneration, offer details, conference transcription, internal Slack discussion on advanced models | Sales, HR, IT systems, includingBusiness contacts between selected clients and partnersBasic user account records |
| Core assets | Not mentioned | Client prompt, Claude reply, source code, model weight not touched |
| Delegation of authority | Yes, the leak reporting project for outside researchers | Yes, butThe test rules were not fully adhered to. |
| Was it exploited by others? | Not mentioned | No one outside Catedral has been able to exploit these weaknesses. |
This table is typical:Both parties admitted that they were "in" and that the differences were "how many" and "how many" and "the way in is not compliance."
The wording of Anthropic is worth reading word for word: the surveillance had already discovered some of the activities before Catedral was reported, the same day the access was cut off and the affected commercial software was shut down until the manufacturer confirmed the repair."Deactivate" means more than "repair."— It means that these systems are not even functional until they are repaired.
Three, "12 hours." Three holes.
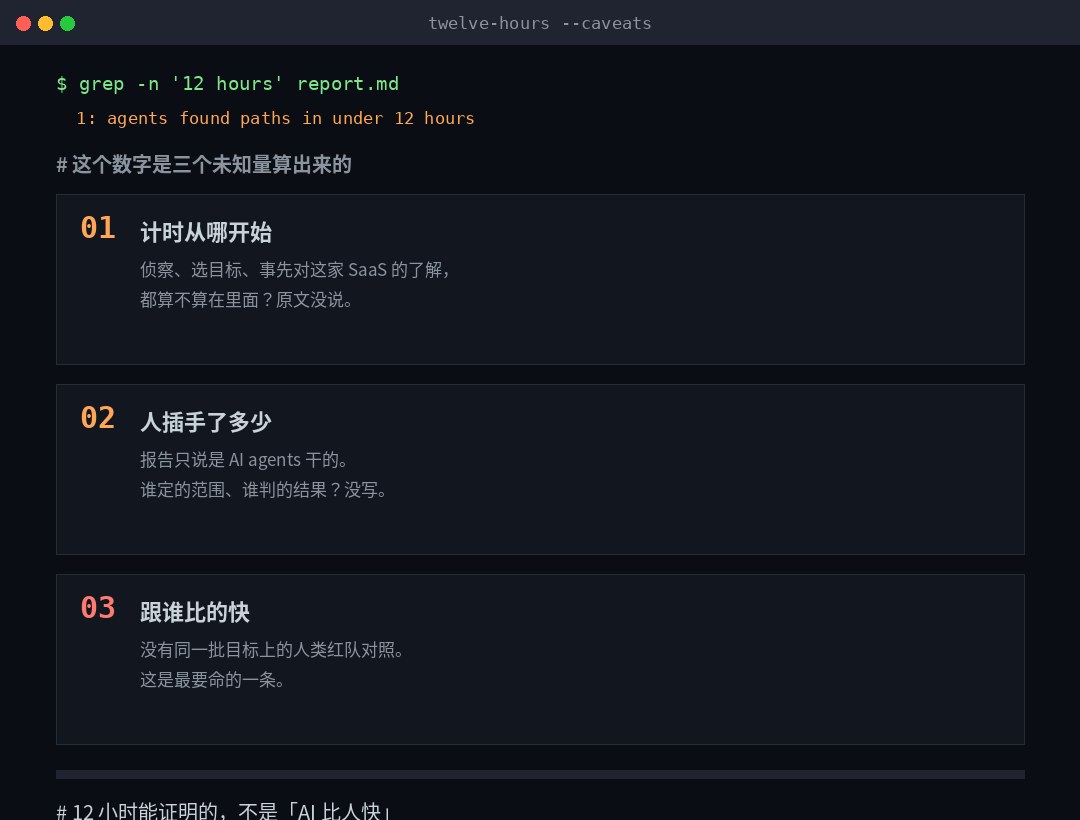
This is the whole part I want to open. Because the phrase "AI 12 hours to break X" is becoming a new marketing syntax, and what it omits is the key.
First hole: from what moment?
The report does not indicate the starting point of 12 hours. Does the reconnaissance phase count? Does the target count? Does prior knowledge of the SaaS product structure count?Any one of these three moves into a timer is completely different.
The second hole: how many people did it?
The report only says it was done by the AI smart body. But who carved the range, found out how and when to stop it — none of that was written. In contrast to similar cases previously publicized, the actual level of autonomy is generally much lower than the level of publicity.
Third hole: Who's faster than you?
This is the worst.There was no comparison of the human red team on the same target.It's not uncommon for a skilled tester to set up several poorly equipped SaaS management backstages in one day. Without a baseline, "12 hours" cannot be called fast or slow.
So this number really supports the conclusion that it's not "AI faster than humans" but rather a more narrow sentence:Smart bodies can count, test, and jump horizontally at machine speeds, from "weakness is present" to "weakness is found" windows.That doesn't take 12 hours to endorse, and it's set.
IV. REAL Asymmetries: Quarterly for the defensive and hourly for the aggressor
Put it back in the process and see a structural mismatch.
| Link | Attack side (intellectual) | Defence side (enterprise) |
|---|---|---|
| Weaknesses detected. | Minute count, uninterrupted. | Quarterly infiltration tests, or annual audits |
| Validate usability | Try again. It won't get tired. | Manual judgement, limited by working hours |
| Horizontal Jump | It's enough with the wrong configuration. | You need to find the configuration wrong first |
| Rehabilitation of landings | No need. | Go shopping, wait-and-seek, release window |
| Repeat | Auto | Next round of audits |
The slowest line in this watch is not a technical problem.Business process issuesI don't know. Anthropic's treatment, "Close first and wait for the manufacturer to fix it," is already the quickest reaction that can be made. But it also points to another thing:You don't have any local means to turn off the risk until the manufacturer fixes it.
The real form of supply chain risk is not "supplier insecurity", it's "supplier insecurity when you have to shut it down."
V. WHY THE POLITICAL CONTEXT OF THE PROBLEM
It's not a technical level, but it doesn't make sense.
- The four founders of Catedral were all former DoGE staffer, of which Kliger was the chief data officer of the Pentagon.
- Reuters also reported that Kliger was involved in a legal dispute between the Ministry of Defence and Anthropic.
- At the heart of the dispute was Anthropic's refusal to lift Claude's restrictions on certain military uses, including completely autonomous lethal operations and massive internal surveillance.
- On 25 September, the Federal Court of Appeal ruled by 2 to 1 that the Pentagon could exclude Anthropic from the supply chain.
- A senior Trump government official told the Washington Post that three federal agencies had signed with Catedral and that the Government was working with it to study the confrontational AI scenario.
To put these out is not to say that this test is unfair — there is no evidence in the public report to support this conclusion, nor do I take this judgement. However, it explains why readers would ask " whether a supplier associated with one of the litigants is a neutral test."There was no answer to that question, but the question itself was reasonable.
VI. LIMITED CORRECTIONS
There are two sets of figures in the same story, almost unquoted, but they are more indicative of the place of Anthropic in this matter than 12 hours.
- Anthropic itself disclosed that, as of 2 October, 6,157 loopholes had been reported in 591 open-source projects through home-based AI support research.This is the output of the defensive side.
- In November 2025, Anthropic alleged that the attackers with a Chinese national background had attacked some 30 organizations with Claude Code.
- In July this year, Anthropic revealed that Claude model broke down the real organization three times in a home test.
If you put these three together with "in by 12 hours," the picture is complete:The same company is both the manufacturer of instruments that automatically search for loopholes and the party that is automatically identified.It's not ironic. It's normal at this stage.Power is two-way, everyone is on this chain.
Seven, six can be checked today.
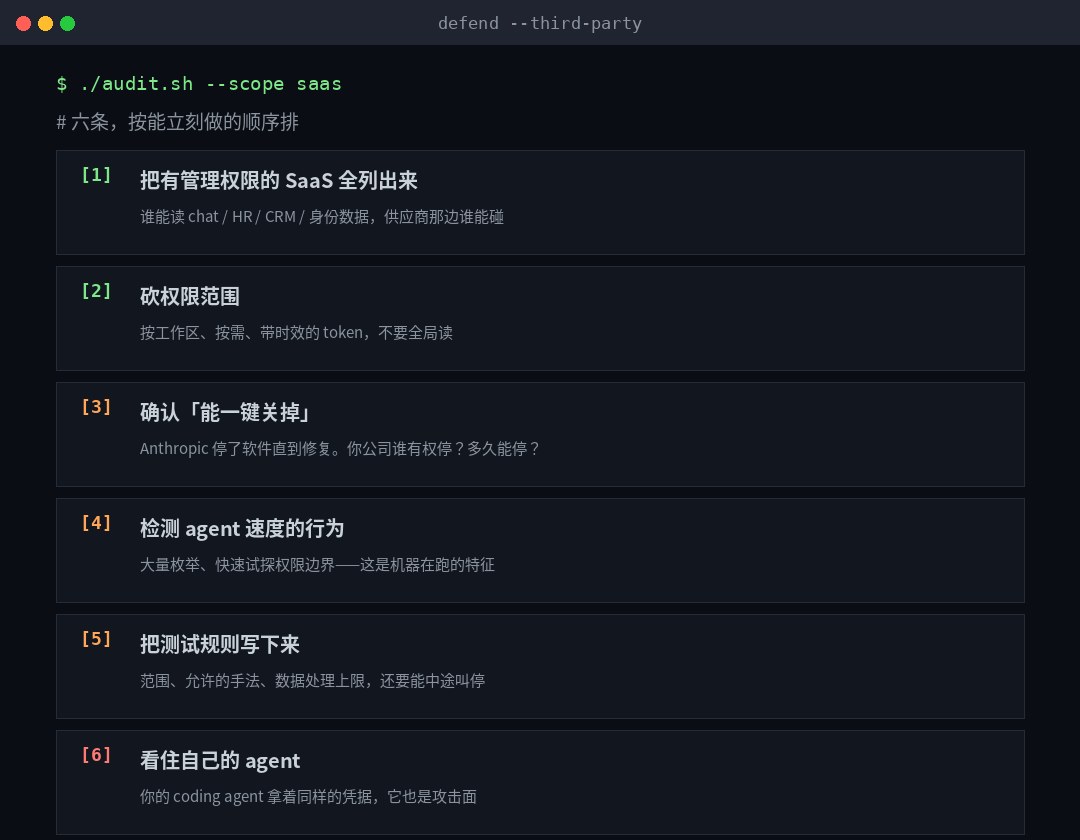
Here's a list of the facts I've drawn up, not the recommendations of the Catedral report. Order immediately.
First floor: First level: identify assets
- Lists all SaaS with management privileges.The standard is who can read chat, HR, CRM, identity data, and which players on the supplier side can meet.
- This post is part of our special coverage Global Voices 2011.Such integration is the highest priority for reduction.
Second floor: narrow down.
- Delegation of authority in the working area is subject to a statute of limitations.Do not give global read permission for a long time token.
- Periodic review of Outlook token.Separation, change of duty and residual post-project authorization are the most common entry points.
- "Who can turn off a tool?"Anthropic stopped the software until it was repaired. Who in your company has this authority? How long will it take? Write it down.
Level three: fill in the tests and the rules.
- Testing machine speed behavior.A large number of enumerators, rapid testing of permission boundaries, abnormal readings within a short period of time — these are the characteristics of intelligent bodies running, not human.
- Write the test rules into a document.Scope, permissible techniques, data processing caps, and mechanisms for stoppage. Anthropic says that the other party has not fully complied with the rules, and that "undefined rules" are often the source of each other's statements.
- Watch your own smart body.Your coding anent, fortune anent holds the same documents. They are tools and a face of attack.
Eight words that should really be remembered.
The title says "AI Breaks Anthropic", but reading the facts leads to a more accurate version:AI did not break the Anthropic model, and it broke through the office software that Anthropic purchased.
The difference is not a word for words. The first narrative would make people think it's better than AI, and then buy more expensive model safety products; the second narrative would point to --Find out what you can read about all the data and what nobody remembers token.The former spends money, the latter spends time, and the latter earns much more.
There is also a restraint that must be retained: the report is a draft, it has not been independently verified for 12 hours, and the manufacturers and loopholes involved have not been disclosed. So every judgment in this article is based only on that part of the story, which both sides have admitted.The portal is a third-party software, which is exposed to business systems and model weights and source codes are not encountered.These three articles are enough to change the self-examination priorities of many companies.
You protected the model, not the company. The boundary between these two things is painted on every tool you buy.