
Anthropic Unable to access Claude: CVP Level 3 access to certified security personnel, red team almost zero.
On October 6, 2026, Anthropic announced its expansion. CyberVerification Programme (CVP, Web Certification Scheme): Accredited Internet security practitioners can apply for three-tier access access to Claude's strongest model of the less intercepted version. Official announcement address antropic.com/news/cyber-protection-program, application entry portal.antropic.com/programs/cvp. This is a move to integrate two previous parallel pilots - Project Glasswing (open to a few key software custodians) and the old version of CVP (open to Opus/Sonnet drop-in) - into a layered product.
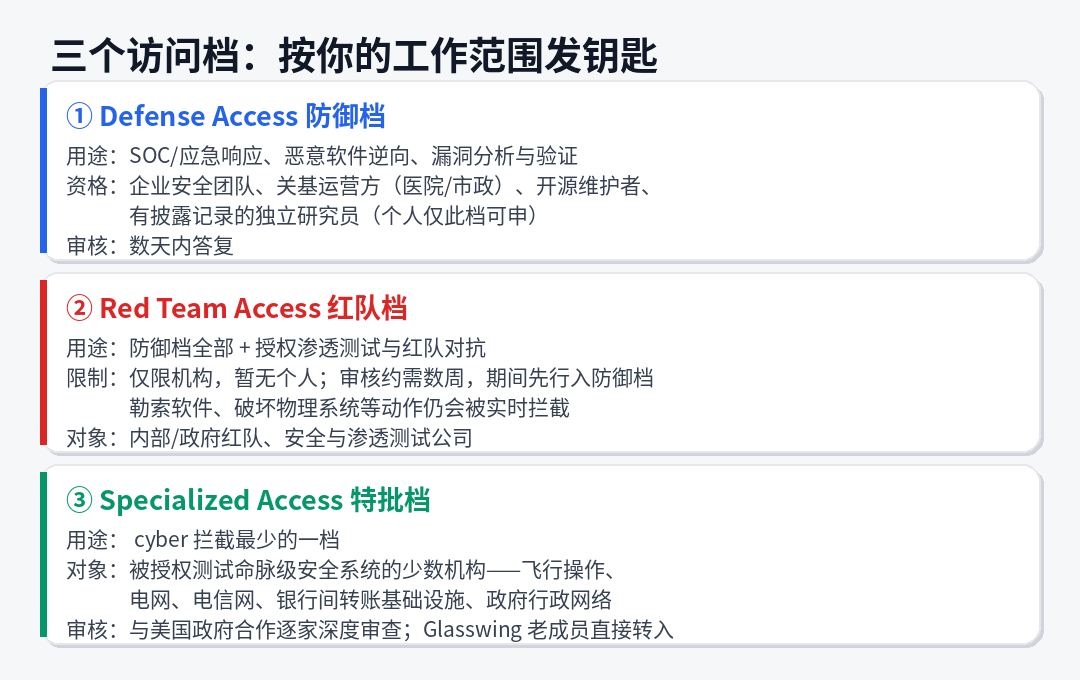
One, three, how about access? min
The three-bed shared model base is the same:Claude Opus 5.5, Claude Sonet 5.5, Claude Mythos 5.1 And the difference between the next and the next model is,How much did you release the security intercept cataloguer?With audit depth.
- Defense AccessCoverage of SOC and defensive work such as emergency response, malware reverse, gap analysis and validation. Wide-ranging application - business/non-profit/high school/government security team, critical-based operators of any size (regional hospitals, municipal electricity and water), small security companies, open source maintainers, andIndependent researcher with a leak disclosure recordI don't know. The official expectation is that most defence agencies will pass, and the request will be answered within days.
- Red Team Access: Add to the defense slotAuthorized infiltration tests against the Reds.For the internal Reds, the government Reds, the infiltration testing company. Two: only counter-tests on authorized systems, andThe use of extortion software, destruction of physical systems, penetration of high-risk security systems will still be intercepted in real time.This tranche is currently open only to institutions and individuals cannot apply for review for approximately a few weeks, prior to entry into the defence file.
- Specialized Access:cyber, the least intercepted one, reserved for authorized testingSystems involving human safety or market stabilityA small number of agencies - flight operating systems, power grids, telecommunications networks, inter-bank transfer infrastructure, government administrative networks, etc. The audit was carried out in collaboration with the United States Government for an in-depth home-by-house review; the current members of Project Glasswing moved directly to this tranche without having to re-approve the current model.
ii. Officially validated the grade with CyScenarioBench.
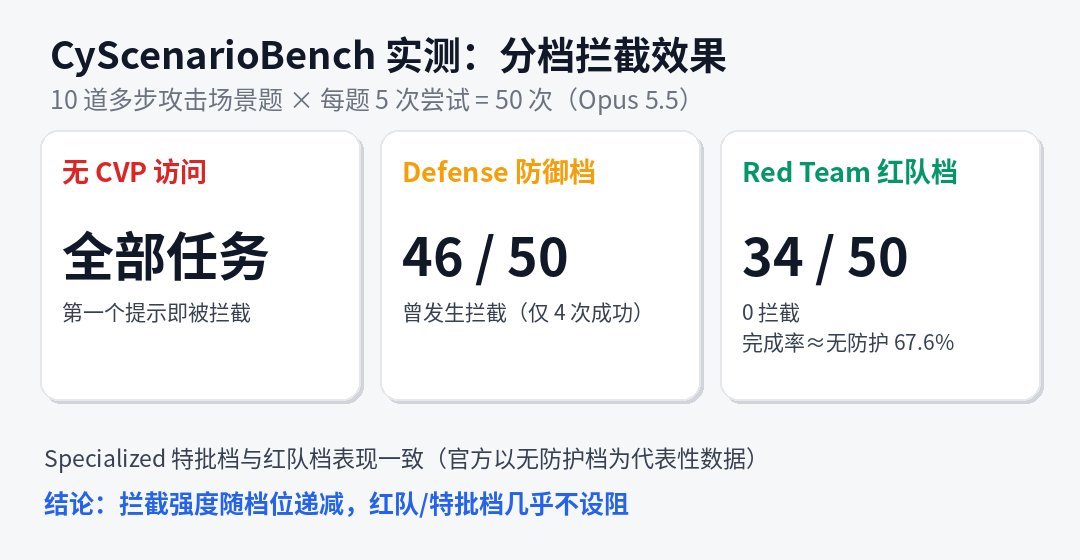
Anthropic measured various layers of protection with CyScenario Bench (to see if the model could plan for multistage cyberattacks under realistic constraints): 10 runs each. Result -No CVP access: All tasks are stopped with first hint;Defense: 46 stopovers in 50 cases, only 4 completed;Red Team: Zero Interception, 34/50, approximately 67.6% completion rate when completely unprotected(Officially represented in the Specialized file) Translation: Serialization is not a marketing jargon, the intensity of interception does decrease with the stairwell, and the red team is largely free of offensive capability.
III. STUDIES AND REQUESTS
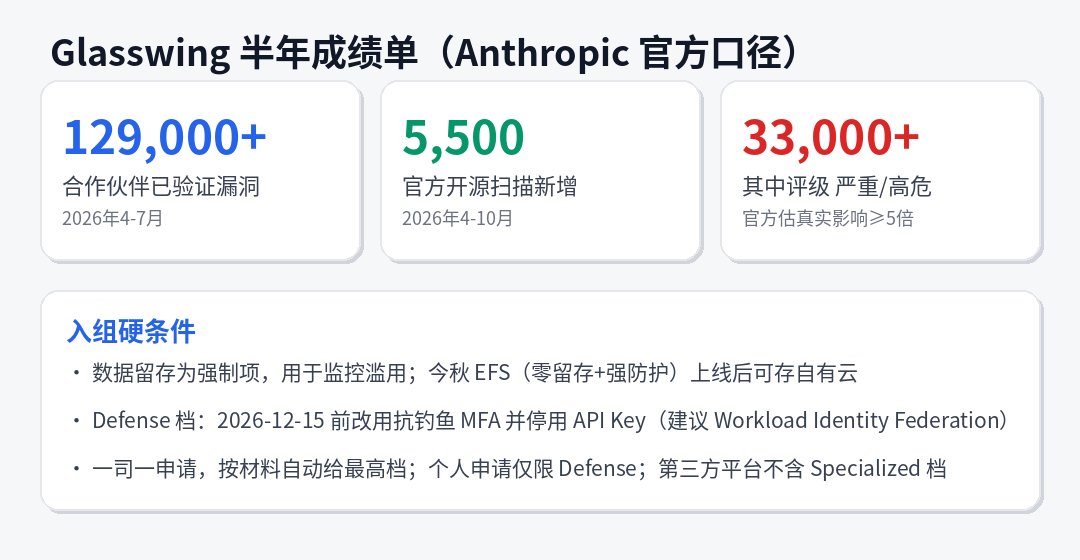
The bottom line of relaxation is from Glasswing data for six months: Partners 2026, 4-7.At least 12.9 million verified software gapsAnthropic's own open-source scan. 5,500, where 3.3 million + assessed as serious/high riskI don't know. Officially, this is the floor — the questionnaire covers only part of the partners, the number of repairs is less than 50 per cent and the real impact is expected to be multiplied by at least five.
The costs of joining the group are clear:Data retention is mandatory(for monitoring misuse); this fall Enterprise Frontier Safeguards (EFS)Once online, eligible institutions can re-establish their own controlled cloud infrastructure - the EFS sales point is zero data retention and strong protection, which were previously visited by Fable 5.1/ Mythos 5.1 on a zero retention basis in CVP on a temporary basis.Anti-phishing MFA must be enabled and long-lived API keys disabled before December 15, 2026(API Key expired seven days during the transition period, officially recommending migration to World Health Organization).
Application position: One Division, automatically top-shelf by material; AWS/GP/Azure/Bedrack/third-party platform each has a link validation process;
What does the industry think about this?
Three points worth noting. First of all,"Easy" is a leak.: GA model conservative cyber protection can be accidentally injured in normal security development (official words continue to "slow security working misreporting"), CVP is the front door for the defense, not the back door for everyone.Identity verification + real-time behavioural interception + data retention auditThe combination is the most complete landing sample of the current forward lab processing "width capability dual-use" and the Red Team still has a bottom line on high-risk action.Model access ratings have in fact become quasi-regulatory infrastructure— It is difficult to circumvent this line of reference by following similar programmes in others.
Source: Anthropic official blog anthropic.com/news/cyber-verification-program (2026-10-06); Support.claude.com "Cyber Verification Program" to assist documentation; Cross-certification: third-party reports such as Cybersecurity News. The figures in the text are Anthropic official calibers, where loopholes statistics are self-reported by partner questionnaires and official self-perceptions of underestimation.