
OpenClaw 4.14: Shipped While Asleep, 20+ Fixes
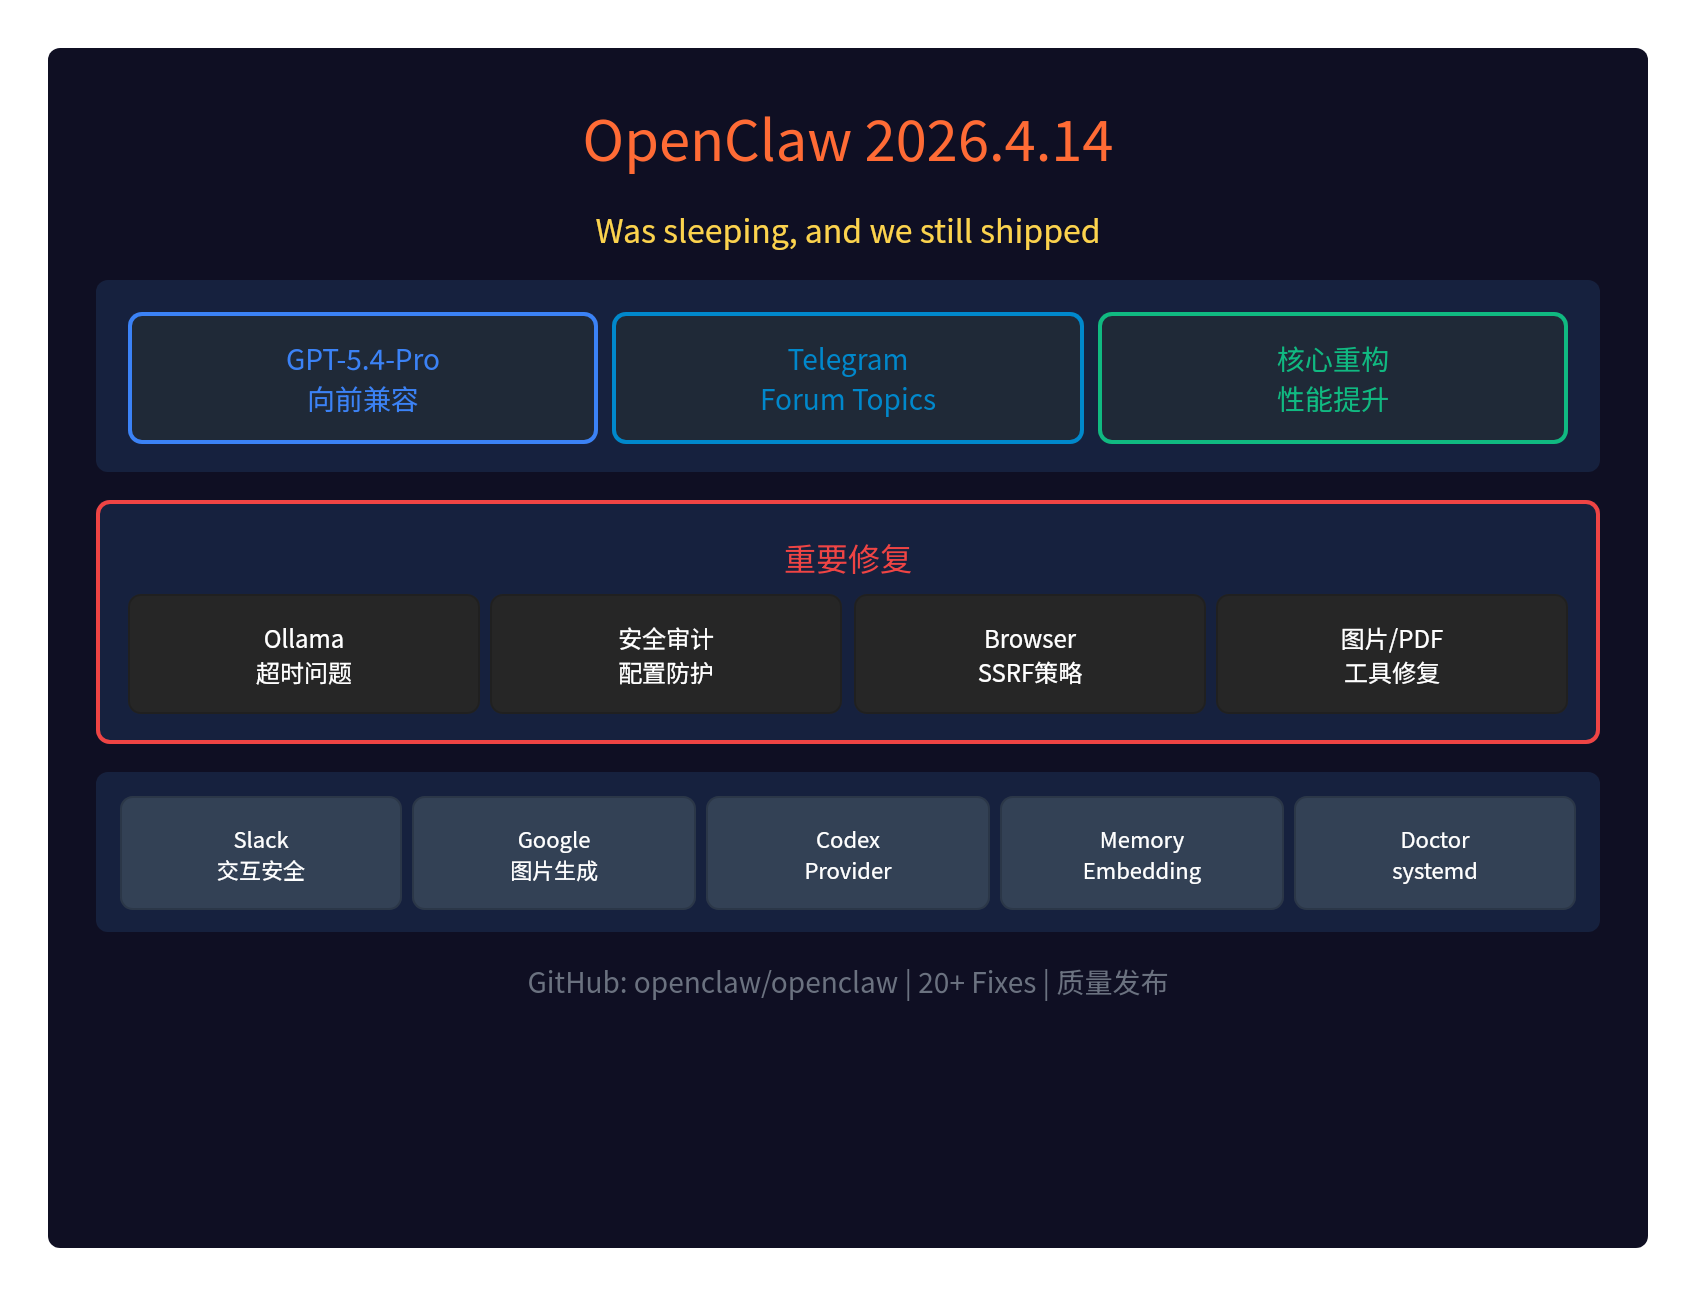
🔥 OpenClaw 4.14 Update: Shipped While Asleep
The official post said it all: "Was sleeping, and we still shipped." — they shipped a release in their sleep.
OpenClaw 2026.4.14 is a broad quality release, focused mainly on model provider improvements and channel provider fixes, plus a refactor of the core codebase for better overall performance.
🎯 Key Improvements
1. GPT-5.4-Pro Forward Compatibility
OpenAI Codex/models gained forward-compatibility support:
- Support for the gpt-5.4-pro model
- Including Codex pricing/limits
- List/status visible before the official catalog updates
Even before OpenAI updates its official model catalog, OpenClaw users can start using GPT-5.4-Pro early.
2. Telegram Forum Topics Improvements
Telegram forum topic support got a major upgrade:
- Human-readable topic names: shown in Agent context, prompt metadata, and plugin hook metadata
- Learning from service messages: topic names are learned automatically from Telegram forum service messages
- Persistent storage: learned topic names survive restarts
3. Core Code Refactor
The underlying core codebase was refactored:
- Performance: overall performance improvements
- Code quality: core modules restructured
🔧 Notable Fixes
| Fix | Description |
|---|---|
| Ollama timeouts | local Ollama runs no longer inherit the default stream cutoff |
| Codex apiKey | fixed the Pi ModelRegistry validator rejection |
| Image/PDF tools | Ollama vision models are no longer rejected as unknown |
| Slack interaction security | fixed interactive triggers bypassing the allowlist |
| Attachment paths | realpath errors no longer downgrade security checks |
| Gateway-tool security | rejects dangerous config changes (like dangerouslyDisableDeviceAuth) |
🔒 Security Fixes
Gateway-tool security audit protection
Gateway-tool now rejects dangerous config changes:
- dangerouslyDisableDeviceAuth
- allowInsecureAuth
- dangerouslyAllowHostHeaderOriginFallback
- hooks.gmail.allowUnsafeExternalContent
- tools.exec.applyPatch.workspaceOnly: false
Flags already enabled stay as they are, but newly enabling a dangerous flag is rejected.
Slack interaction security
Slack interaction events now:
- Apply the configured global allowFrom owner allowlist
- Require the expected sender id for cross-validation
- Reject ambiguous channel types
🌐 Browser SSRF Fix
Browser SSRF policy fixes:
- Hostname navigation restored: works again under the default SSRF policy
- Strict mode stays reachable: set explicitly via config
- CDP control unaffected: the local CDP control policy is independent
📝 More Fixes
Other notable fixes include:
- Google image generation: fixed Gemini image requests 404ing
- Memory embeddings: fixed the missing proxy prefix
- Doctor/systemd: no longer embeds dotenv-backed secrets
- GitHub Copilot thinking: gpt-5.4 can now use xhigh reasoning
- Ollama/OpenAI-compat: sends stream_options.include_usage
- Telegram media downloads: fixed DNS issues behind proxies
- Media-understanding/proxy env: fixed DNS pre-resolution failures behind proxies
- Onboarding/custom providers: validation probes now use max_tokens=16
📝 Summary
OpenClaw 2026.4.14 is a quality release:
- GPT-5.4-Pro forward-compatibility support
- Major Telegram Forum Topics improvements
- Core code refactor with performance gains
- 20+ fixes covering Ollama, Codex, Slack, Browser, and more
- Security audit protection that rejects dangerous config changes
Shipped a release while asleep — that's just how OpenClaw rolls.
GitHub Releases:https://github.com/openclaw/openclaw/releases